crownsplitter@kali: ~

# This shell is interactive with JavaScript enabled. Here is everything it can show:

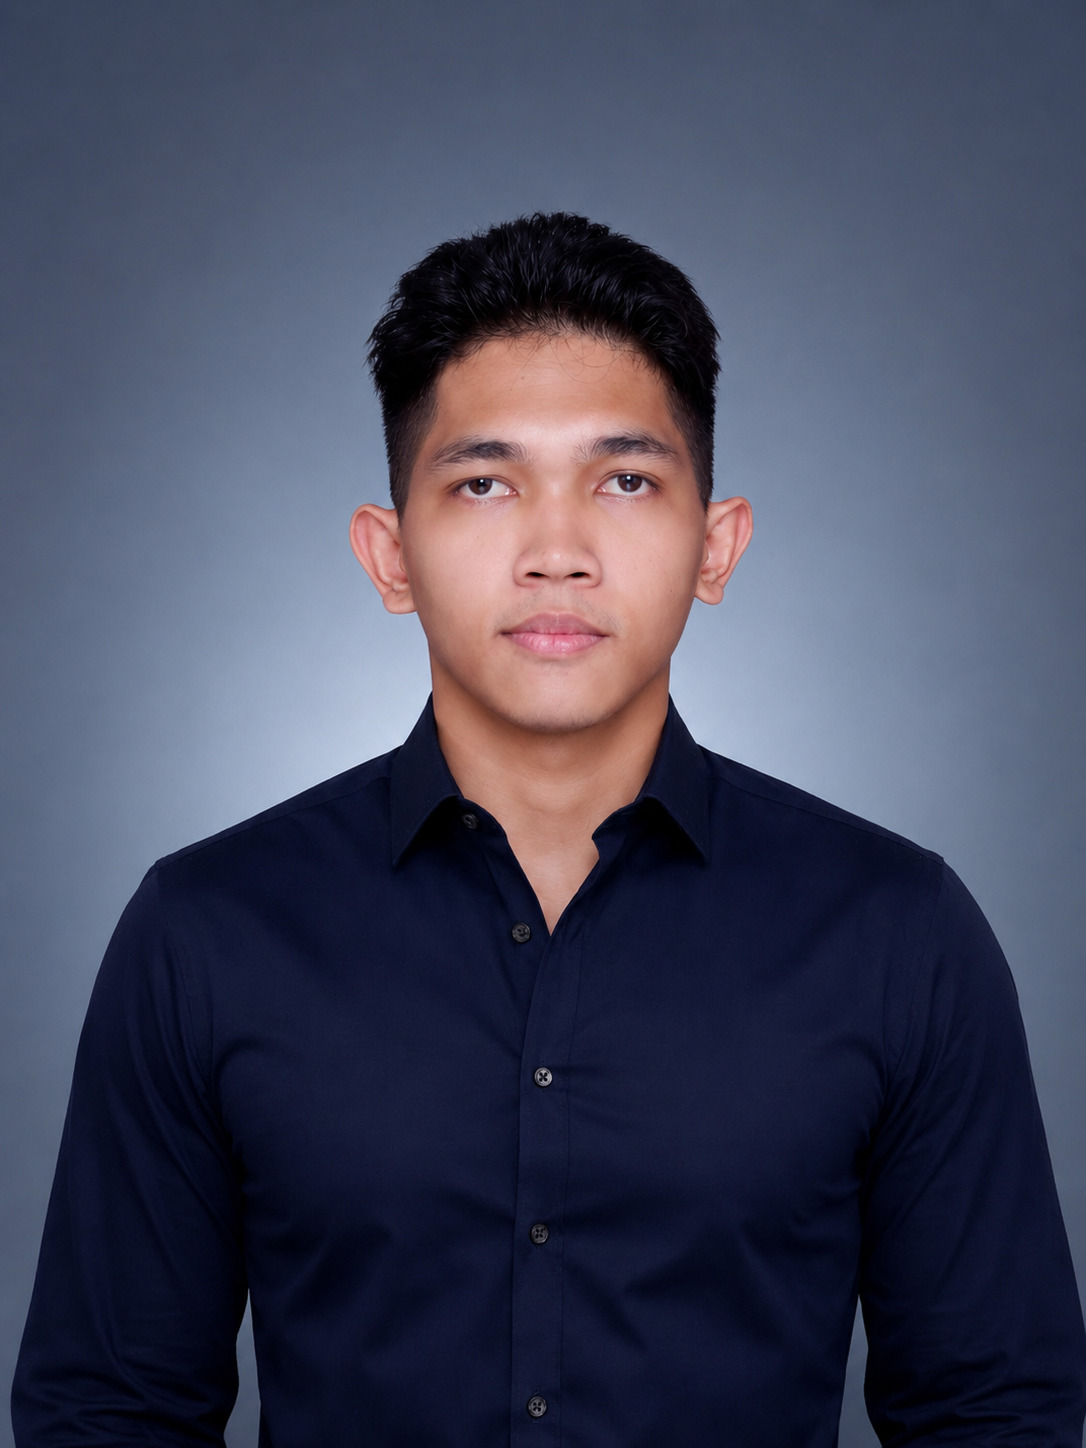
Portrait of Rivaldo Dominggos Pardede

Rivaldo Dominggos Pardede

Junior Penetration Tester · Red Team @ Temika Cyber

Red Team — Web, Mobile & Infrastructure Security · Bandung, Indonesia · since Aug 2026

Offensive security. I break access controls and write up exactly how.

download CV (pdf)

about

I'm a penetration tester on Temika Cyber's Red Team, based in Bandung, Indonesia — web, mobile, and infrastructure assessments against the OWASP WSTG and MASTG, with remediation retesting to confirm fixes actually hold.

My route here wasn't the usual one. I built mobile and backend applications first — Flutter, Dart, Node.js, Firebase, on-device ML — so I read applications from the inside out: how they're wired, where trust boundaries get assumed instead of enforced, and which "impossible" states nobody tested.

That builder's instinct is what I now point at access control, authentication, and business logic. I found and responsibly disclosed a Critical (P1) account-takeover chain in a production university portal, won first place at a national cybersecurity CTF, and reached Professional rank (Top 5%) on Hack The Box Academy. I still run CTFs and bug bounty outside work.

how I got here

  1. 2022 – 2026
    Computer Science @ USU — and shipping apps

    B.Sc. Computer Science (GPA 3.96/4.00). Backend Development Trainee at IDCamp (Node.js REST APIs, auth). Built and shipped multiple Flutter apps — the build background that now informs how I test.

  2. 2024 – 2025
    Security-curious → hands-on, and teaching

    Networking and offensive fundamentals: Cisco Networking Academy, TryHackMe (47 rooms, Top 15%), LetsDefend (SOC/blue-team). Served as Computer Networking Lab Coordinator at IKLC/USU — teaching TCP/IP, subnetting, and Wireshark traffic analysis to 20+ students per class.

  3. Jan 2025 – present
    Hack The Box Academy — Professional, Top 5%

    Self-driven offensive training: SQLi, XSS, file upload, command injection, broken auth, session security, GraphQL, ffuf enumeration — plus defensive modules (SIEM, Windows event logs, forensics). From Jan 2026, the Hextree Android security path (JADX, APKTool, Frida).

  4. Aug 2025
    1st place — national cybersecurity CTF

    First place at "Siber Tangguh Bangsa Merdeka" 2025, a team-based CTF focused on web security and attack-surface exploration.

  5. Mar 2026
    Critical (P1) account-takeover disclosure

    Discovered and responsibly disclosed a Critical account-takeover on a USU production student portal via chained IDOR + broken access control, with a Burp Suite proof-of-concept. Received an official Certificate of Appreciation from PSI USU.

  6. Aug 2026 – present
    Junior Penetration Tester @ Temika Cyber

    Joined Temika Cyber (PT Teknologi Integrasi Informatika) on the Red Team: professional web, mobile, and infrastructure penetration testing under NDA.

experience

Junior Penetration Tester, Red Team Aug 2026 – present

Temika Cyber · PT Teknologi Integrasi Informatika · Bandung, Indonesia (on-site)

  • Mobile application penetration tests following the OWASP Mobile Application Security Testing Guide (MASTG).
  • Web application penetration tests following the OWASP Web Security Testing Guide (WSTG).
  • Retest web applications and infrastructure to validate remediation of previously reported findings.
  • Document findings with impact, reproduction steps, and remediation guidance.
  • Preparing for upcoming wireless (Wi-Fi) penetration testing.

Engagement specifics are covered by confidentiality — what's shown here is scope and method, never client or finding detail.

Laboratory Coordinator, Computer Networking Jan 2025 – Jun 2025

IKLC — Universitas Sumatera Utara · Medan, Indonesia

  • Supervised hands-on networking labs (TCP/IP, subnetting, routing) for 20+ students per class.
  • Guided students analyzing network traffic with Wireshark, connecting theory to real behavior.
Backend Development Trainee Dec 2023 – Feb 2024

Indosat Ooredoo Hutchison (IDCamp) · Remote, Indonesia

  • Built backend applications with Node.js: RESTful API design, authentication, basic cloud services.
  • Server-side fundamentals that inform how I reason about client–server trust.

disclosed findings & wins

P1 · CRITICAL account-takeover.md

Account Takeover — IDOR + Broken Access Control

Mar 2026 · OWASP A01:2021 · Burp Suite · manual recon

Chained an IDOR pattern in user-scoped requests with a broken access-control check to reach full account takeover on a USU production student portal (mahasiswa.usu.ac.id). Built a Burp Suite proof-of-concept, then reported through responsible disclosure with impact statement and remediation guidance. Received an official Certificate of Appreciation from Pusat Sistem Informasi USU.

Certificate of Appreciation — PSI USU →

1st PLACE siber-tangguh-2025.md

National Cybersecurity CTF — "Siber Tangguh Bangsa Merdeka" 2025

Aug 2025 · team-based · web security

First place in a national, team-based Capture The Flag competition focused on web security fundamentals and attack-surface exploration.

Certificate →
training platforms

public profiles — no re-hosted platform badges

Hack The Box Academy — Professional rank, Top 5% global view profile →
TryHackMe 47 rooms · Top 15% · 10 badges view profile →
LetsDefend SOC & blue-team fundamentals view profile →

certificates & badges

Certificate of Appreciation — Critical Vulnerability Disclosure USU — Pusat Sistem Informasi — Responsible disclosure of a P1 account-takeover. open →
1st Place — Siber Tangguh Bangsa Merdeka 2025 National Cybersecurity CTF open →
IDCamp 2025 — Multiplatform App Developer (Expert / Mahir) Indosat Ooredoo Hutchison — 230+ hours, Expert track. open →
Pre Security Path Certificate TryHackMe open →
CPTS & CRTP — in preparation (not yet earned) Hack The Box / Pentester Academy — Listed for transparency; currently studying toward these. in progress

tools & methodology

web app security

OWASP Top 10OWASP WSTGIDORBroken Access Control (A01)XSSSQL InjectionCommand InjectionFile UploadCSRFBroken AuthSession SecurityGraphQL

mobile app security

OWASP MASTGAndroid RE (JADX, APKTool)FridaBurp SuitemitmproxyIntent attack surfaceBroadcast Receiver security

tools

Burp SuiteNmapWiresharkffufSQLMapGobusterHashcatJohn the RipperEvil-WinRMLinux CLIGitADB

infra & process

Vulnerability assessmentRemediation retestingVAPTResponsible disclosurePentest reportingCVSSMITRE ATT&CKOWASP ASVSNIST CSF

blue team

SIEM fundamentalsIncident handlingWindows event logsDigital forensicsPhishing analysis

networking

TCP/IPSubnettingRoutingDNSHTTP/HTTPSTraffic analysis

build background

FlutterDartNode.jsFirebase / Firestore rulesOn-device ML (TFLite)REST APIsPythonBashPowerShell

mobile development

the build background — a differentiator, not the headline. each opens a detail page.

education

B.Sc. Computer Science Aug 2022 – Jan 2026

Universitas Sumatera Utara (USU) · GPA 3.96 / 4.00

Thesis: a hybrid cryptographic system proof-of-concept (XRSA + modified Salsa20) — key management, authentication, and security/performance trade-offs.

Responsibly disclosed a P1 vulnerability in a USU production portal during this period.

contact